
[Video] ‘Learning Cyber Security’ Writeup – Tryhackme

Learning Cyber Security Get a short introduction to a few of the security topics you’ll be learning about. Task 1 Web Application Security Why understanding how the web works is important   To attack web applications, you need to understand how they work. Hacking websites isn’t some magical process but does come down to knowing … Read more

[Video] ‘Snapped “Phish”-ing Line’ Writeup – Tryhackme

Snapped “Phish”-ing Line Apply learned skills to probe malicious emails and URLs, exposing a vast phishing campaign. Task 1 Challenge Scenario Based on real-world occurrences and past analysis, this scenario presents a narrative with invented names, characters, and events. Please note: The phishing kit used in this scenario was retrieved from a real-world phishing campaign. … Read more

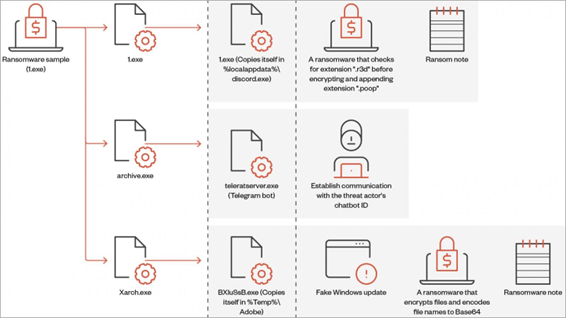
Big Head ransomware za vrijeme enkripcije prikazuje lažno Windows ažuriranje [cert.hr]

Trend Micro je objavio tehničko izvješće o novom ransomwareu nazvanom ‘Big Head’, čije je ranije inačice istraživao i Fortinet. Tvrde da sve tri inačice potječu od istog aktera koji prilagođava pristup napada. Za vrijeme kriptiranja podataka korisniku na prikazuje lažni proces ažuriranja Windowsa. Big Head je .NET binarna datoteka koja instalira tri kriptirane datoteke na … Read more

“Charming Kitten” hackere bruger ny ‘NokNok’ malware til macOS [cert.dk]

I relation til phishing og social engineering metoder der anvendes i denne kampagne, udgiver hackerne sig for at være atomeksperter fra USA og henvender sig til ofre med et tilbud om, at gennemgå et udkast om udenrigspolitiske emner. I mange tilfælde indsætter angriberne andre personer i koorespondancen for at give karakter af legitimitet og etablere … Read more

A Network of SOCs? [cert.at]

Preface I wrote most of this text quickly in January 2021 when the European Commission asked me to apply my lessons learned from the CSIRTs Network to a potential European Network of SOCs. During 2022, the plans for SOC collaboration have been toned down a bit, the DIGITAL Europe funding scheme proposes multiple platforms where … Read more

Google patcher udnyttede sårbarheder i Android [cert.dk]

Google har her i juli udsendt sikkerhedsopdateringer til Android, der retter 46 sårbarheder, hvoraf tre er udnyttet in-the-wild. Det skriver Bleeping Computer og Security Week m.fl. på baggrund af en sikkerhedsbulletin fra Google. Sprog Dansk Keywords:  sårbarheder opdateringer Læs mere om Google patcher udnyttede sårbarheder i Android Source: Read More ​ Nyheder fra DKCERT

Jobopslag: DKCERT søger sikkerhedsspecialist [cert.dk]

DKCERT søger en cyber- og informationssikkerhedsspecialist til sit sikkerhedsteam. Stillingen rummer store mulighed for kompetenceudvikling og opbygning af netværk blandt ligesindede i Danmark og internationalt. Sprog Dansk Keywords:  DKCERT DTU Læs mere om Jobopslag: DKCERT søger sikkerhedsspecialist Source: Read More ​ Nyheder fra DKCERT

Tilmelding til DeiC-konferencen er åben [cert.dk]

Hvordan får du en uagtsom medarbejder med ind i din risikovurdering? Hvad skal den nye decentrale enhed for cyber- og informationssikkerhed i Uddannelses- og forskningsstyrelsen lave? Vil du høre truslerne, imødegåelse af DDoS-angreb, ISO27001 og ISO27005? Der er nok af relevante emner for sikkerhedsmedarbejderen, CISO’en og alle andre med interesse i sikkerhedsarbejdet på årets DeiC-konference, … Read more

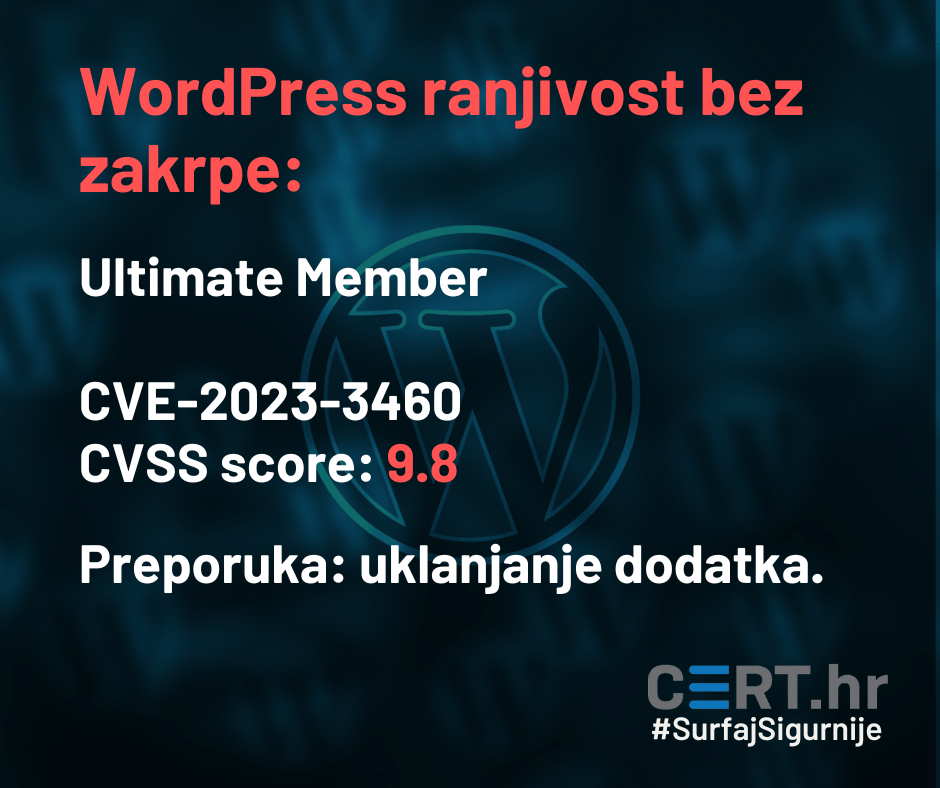
Otkrivena je kritična ranjivost ‘Ultimate Member’ WordPress dodatka. Zakrpe nema. [cert.hr]

‘Ultimate Member’ je dodatak koji omogućuje registraciju i upravljanje zajednicama na WordPress stranicama. Kritična ranjivost (CVE-2023-3460) ‘Ultimate Member’ WordPress dodatka dobila je ocjenu 9.8. Ranjive su sve verzije dodatka koji broji više od 200 000 aktivnih instalacija. Iskorištavanjem ove ranjivosti, napadač može registrirati nove admin račune. Ranjivost su pokušali otkloniti veće nekoliko puta, ali još … Read more

Supply chainangreb får ram på TSMC [cert.dk]

Det er tilsyneladende et supply chain-angreb, der er årsagen til, at verdens største chipproducent, TSMC, har været at finde på ransomware-gruppen LockBits lækagested og angiveligt er blevet afkrævet en løsesum på 70 millioner dollar. Det skriver Infosecurity Magazine. Dagen før at TSMCs navn dukkede op på lækagestedet, begyndte en trusselsaktør kendt som Bassterlord, som er … Read more

Wordpres plugin er under angreb [cert.dk]

Trusselaktører er i gang med at udnytte en kritisk WordPress 0-dagssårbarhed i et plugin. Denne gang er en sårbarhed i det såkaldte Ultimate Member-plugin, som kan anvendes til at oprette administratorkonti. De kan så bruges til at tage fuld kontrol over webstederne. Fejlen har id’et CVE-2023-3460 og en CVSS-score på 9,8. Sprog Dansk Keywords:  WordPress … Read more

Rygte: Kræver 70 mio i løsesum [cert.dk]

Lockbit hævder at have hacket verdens største producent af chips. Det skriver Infosecurity Magazine efter at have fået oplyst, at navnet på Taiwan Semiconductor Manufacturing Company (TSMC) er offentliggjort på Lockbits lækageside i sidste uge. Sprog Dansk Keywords:  afpresning ransomware Læs mere om Rygte: Kræver 70 mio i løsesum Source: Read More ​ Nyheder fra … Read more

Listen over de 25 mest farlige softwarefejl offentliggjort [cert.dk]

MITRE har publiceret dette års liste over de 25 mest farlige sårbarheder, der har plaget software i løbet af de foregående to år. Der skriver Bleeping Computer. Listen er lavet ud fra en analyse af 43.996 CVE-numre, som er udstillet i 2021 og 2022 på National Vulnerability Database med fokus på antallet af sårbarhedstyper, der … Read more

Otkrili smo Zero-day ranjivost Mattermost platforme [cert.hr]

Inženjer za računalnu sigurnost u Nacionalnom CERT-u (F. Omazić) je prilikom testiranja popularne platforme za sigurne komunikacije “Mattermost” otkrio ranjivost nultog dana (zero-day vulnerability). S obzirom na to da se radilo o lokalnoj instanci Mattermost poslužitelja, kao PoC (Proof of concept) izrađena je i zero-day exploit skripta, to jest skripta koja iskorištava pronađenu ranjivost. Prema … Read more

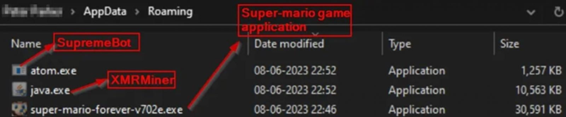
Piratske verzije popularne igre Super Mario, mogu skrivati zlonamjerni kôd [cert.hr]

Skrivanje zlonamjernog kôda unutar legitimnih programa popularna je taktika kriminalnih aktera. Tako su hakeri odlučili sakriti zlonamjerni kôd za rudarenje kripto valuta unutar instalacijskog paketa popularne video igre Super Mario 3: Mario Forever. Ova besplatna verzija računalne igre preuzeta je više od milijun puta. Pobudila je nostalgiju među igračima jer je zadržala mehaniku starije verzije, … Read more

Fortinet je izdao sigurnosne zakrpe za kritičnu ranjivost CVE-2023-27997 [cert.hr]

Fortinet je jučer izdao sigurnosne zakrpe za kritičnu ranjivost (CVE-2023-27997) koja pogađa FortiOS i FortiProxy SSL-VPN. Ranjivost potencijalno omogućuje udaljenom napadaču izvršavanje proizvoljnog programskog koda. Nacionalni CERT preporučuje instalaciju sigurnosnih zakrpa ovisno o trenutnoj verziji koja se koristi. Više o samoj ranjivosti kao i ranjivim verzijama FortOS-a i FortiProxy-a možete pronaći na: https://www.fortiguard.com/psirt/FG-IR-23-097 https://nvd.nist.gov/vuln/detail/CVE-2023-27997 https://www.bleepingcomputer.com/news/security/fortinet-fixes-critical-rce-flaw-in-fortigate-ssl-vpn-devices-patch-now/ … Read more

Sigurnosni rizici pohrane lozinki u preglednike [cert.hr]

Kategorije: EXP Brojni preglednici imaju funkcionalnost pohrane lozinki te sinkronizacije lozinki između različitih uređaja istog korisnika. Iako ta funkcionalnost poboljšava korisničko iskustvo, povećava i rizik od nekih napada. Osobito su opasni scenariji u kojima zaposlenik u pregledniku svog osobnog računala pohranjuje lozinke za pristup poslovnim resursima (npr. lozinku za poslovni mail).U ovom dokumentu su opisane … Read more

[Upozorenje] U tijeku je nova ucjenjivačka kampanja! [cert.hr]

Nacionalni CERT je zaprimio veći broj prijava pokušaja prijevare putem e-pošte. U ovoj vrsti napada, napadač pokušava izazvati strah kod potencijalne žrtve i ostvariti komunikaciju. U nastavku komunikacije žrtvu se traži uplata novca ili kriptovaluta. From: 023001299 Subject: Hitno – odgovorite odmah Tekst poruke: Hakirali smo vašu adresu e-pošte, telefon i elektroniku. A zatim postavio … Read more

[Bug Bounty Money] – Episode 7

XSS vulnerability without a content security bypass in a `CUSTOM` App through Button tag , 2,000 USD Possible XSS vulnerability without a content security bypass, 2,000 USD download file type warning on Windows does not appear if “ask where to save file before downloading” setting is enabled, 500 USD Reset password link sent over unsecured … Read more

Potpisan Memorandum o razumijevanju o suzbijanju kibernetičkog kriminala između SAD-a i Hrvatske [cert.hr]

Republika Hrvatska i Sjedinjene Američke Države potpisale su Memorandum koji će osigurati kvalitetniju suradnju i razmjenu informacija u području transnacionalnog kibernetičkog kriminala. U okviru Međunarodne konferencije o borbi protiv kibernetičkog kriminala koja se u održala u Šibeniku 22. i 23. svibnja 2023. godine, Ministarstvo pravosuđa i uprave, Državno odvjetništvo Republike Hrvatske i Veleposlanstvo Sjedinjenih Američkih … Read more

Apple je izdao zakrpe za tri 0-day ranjivosti [cert.hr]

Ranjivosti su pronađene u Safari pregledniku, točnije u njegovom WebKit pogonu (engl. engine). Zakrpane ranjivosti: CVE-2023-32409, CVE-2023-28204 i CVE-2023-32373. BleepingComputer piše kako je od početka godine, Apple zakrpao čak šest 0-day ranjivosti. Iskorištavanje ovih ranjivosti napadaču omogućuje pristup osjetljivim informacijama i potencijalno izvršavanje zlonamjernog kôda na žrtvinom uređaju. Lista uređaja na koje se odnose ove … Read more

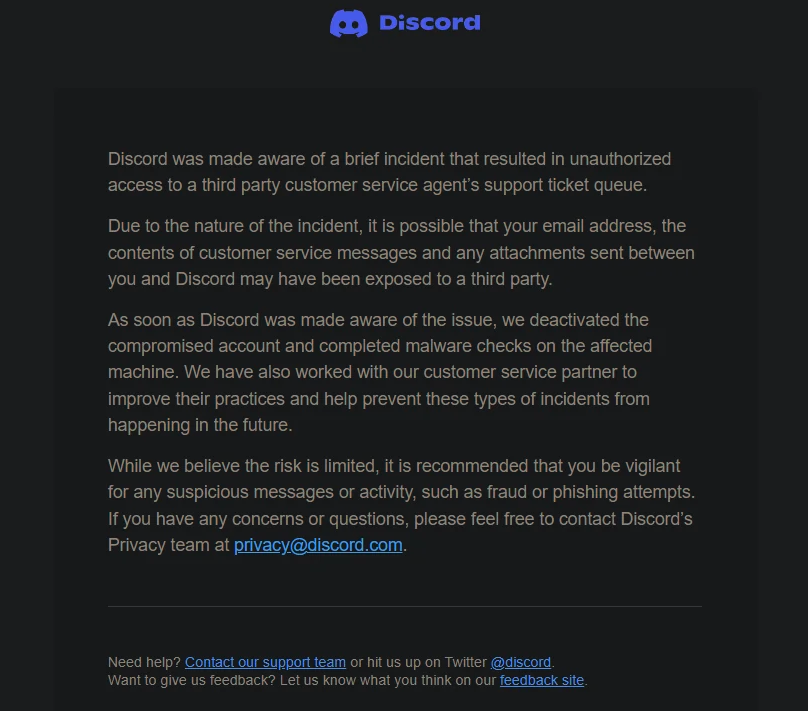
Kompromitirani su podaci korisnika Discorda [cert.hr]

Discord, popularna društvena mreža za dopisivanje i obavljanje poziva, obavijestila je korisnike o povredi podataka nakon kompromitacije računa treće strane. Obavijest Discorda (izvor: bleepingcomputer.com) Kompromitirani su podaci ticket sustava korisničke podrške. Među njima se nalaze adrese elektroničke pošte, poruke koje su korisnici razmijenili s korisničkom podrškom i dostavljeni privici. Kompromitirani račun je odmah deaktiviran, a … Read more

[Bug Bounty Money] – Episode 6 – Week 17 / 2023

[Bug Bounty Money] – Episode 4 – Weeks 14 & 15 / 2023

adding h1_analyst_* to username for normal users , 500 USD UXss on brave browser via scan QR Code, 500 USD Bypass parsing of transaction data, users on the phishing site will transfer/approve ERC20 tokens without being alerted, 1000 USD Ruby’s CGI library has HTTP response splitting (HTTP header injection), leaking confidential information, 4000 USD Use … Read more

[Bug Bounty Money] – Episode 3 – Week 13 / 2023

Open Redirect Vulnerability in Action Pack, 2400 USD Lack of bruteforce protection for TOTP 2FA, 750 USD Arbitrary read of all SVG files on a Nextcloud server, 1250 USD Cards in Deck are readable by any user, 825 USD HTML injection via insecure parameter [https://www.ubercarshare.com/], 650 USD DOM based XSS via insecure parameter on [ … Read more

ChatGPT Plugins: A Revolution in AI Interaction and the Global Implications

Join the waitlist: https://openai.com/waitlist/plugins Exploring the impact of ChatGPT plugins on the world, industries, and individual lives Introduction OpenAI has recently announced the implementation of plugins for ChatGPT, its advanced language model. This groundbreaking development has the potential to drastically transform how we interact with artificial intelligence (AI) and its applications. With a range of … Read more

Novo Portal de Estatísticas do CERT.br [cert.br]

Está no ar um novo portal do CERT.br: Estatísticas Mantidas pelo CERT.br https://stats.cert.br/ Neste portal estão disponíveis diversas estatísticas relacionadas com incidentes de segurança na Internet, sistemas mal configurados passíveis de serem abusados, ataques vistos em sensores (honeypots) e reclamações de spam. As estatísticas são atualizadas mensalmente. Para ser avisado sempre que uma categoria for … Read more

[Bug Bounty Money] – Episode 1 – Week 11 / 2023

Traffic amplification attack via discovery protocol, 2000 USD information disclosure of another company bug on video, 500 USD Stored XSS on www.hackerone.com due to deleted S3-bucket from old page_widget, 500 USD Attacker is able to query Github repositories of arbitrary Shopify Hydrogen Users, 900 USD Delete anyone’s content spotlight remotely., 15000 USD

[Video] “Cyber Kill Chain” Writeup – Tryhackme “SOC Level 1” Learning pathway

The Cyber Kill Chain framework is designed for identification and prevention of the network intrusions. You will learn what the adversaries need to do in order to achieve their goals. Task 1 Introduction The term kill chain is a military concept related to the structure of an attack. It consists of target identification, decision and … Read more

[Video] “Pyramid Of Pain” Writeup – Tryhackme “SOC Level 1” Learning pathway

Learn what is the Pyramid of Pain and how to utilize this model to determine the level of difficulty it will cause for an adversary to change the indicators associated with them, and their campaign.   Task 1 Introduction This well-renowned concept is being applied to cybersecurity solutions like Cisco Security, SentinelOne, and SOCRadar to … Read more

“Junior Security Analyst Intro” Writeup – Tryhackme “SOC Level 1” Learning pathway

Task 1 A career as a Junior (Associate) Security Analyst In the Junior Security Analyst role, you will be a Triage Specialist. You will spend a lot of time triaging or monitoring the event logs and alerts. The responsibilities for a Junior Security Analyst or Tier 1 SOC Analyst include: Monitor and investigate the alerts … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 23] Defence in Depth Mission ELFPossible: Abominable for a Day

Every effort you have put through builds on top of each other to bring you right at this moment. Santa and the security team are so proud of you for sticking around and being with us until now. You’re practically a member of the SSOC team already! There’s just one more thing left to learn: … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 22] Attack Surface Reduction Threats are failing all around me

McSkidy wants to improve the security posture of Santa’s network by learning from the recent attempts to disrupt Christmas. As a first step, she plans to implement low-effort, high-value changes that improve the security posture significantly. Learning Objectives To help McSkidy with her improvements, we will learn some concepts and evaluate some steps to take. … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 21] MQTT Have yourself a merry little webcam

After investigating the web camera implant through hardware and firmware reverse engineering, you are tasked with identifying and exploiting any known vulnerabilities in the web camera. Elf Mcskidy is confident you won’t be able to compromise the web camera as it seems to be up-to-date, but we will investigate if off-the-shelf exploits are even needed … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 20] Firmware Binwalkin’ around the Christmas tree

We can now learn more about the mysterious device found in Santa’s workshop. Elf Forensic McBlue has successfully been able to find the device ID. Now that we have the hardware device ID, help Elf McSkidy reverse the encrypted firmware and find interesting endpoints for IoT exploitation. Learning Objectives What is firmware reverse engineering Techniques … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 19] Hardware Hacking Wiggles go brrr

Spying on Santa Elf McSkidy was doing a regular sweep of Santa’s workshop when he discovered a hardware implant! The implant has a web camera attached to a microprocessor and another chip. It seems like someone was planning something malicious… We must try to understand what this implant was trying to do! We will deal … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 18] Sigma Lumberjack Lenny Learns New Rules

Compromise has been confirmed within the Best Festival Company Infrastructure, and tests have been conducted in the last couple of weeks. However, Santa’s SOC team wonders if there are methodologies that would help them perform threat detection faster by analysing the logs they collect. Elf McSkidy is aware of Sigma rules and has tasked you … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 17] Secure Coding Filtering for Order Amidst Chaos

After handling unrestricted file uploads and SQLi vulnerabilities, McSkidy continued to review Santa’s web applications. She stumbled upon user-submitted inputs that are unrecognizable, and some are even bordering on malicious! She then discovered that Santa’s team hadn’t updated these web applications in a long time, as they clearly needed more controls to filter misuse. Can … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 16] Secure Coding SQLi’s the king, the carolers sing

Set to have all their apps secured, the elves turned towards the one Santa uses to manage the present deliveries for Christmas. Elf McSkidy asked Elf Exploit and Elf Admin to assist you in clearing the application from SQL injections. When presented with the app’s code, both elves looked a bit shocked, as none of … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 15] Secure Coding Santa is looking for a Sidekick

Input Validation Insufficient input validation is one of the biggest security concerns for web applications. The issue occurs when user-provided input is inherently trusted by the application. Since user input can also be controlled by an attacker, we can see how this inherent trust can lead to many problems. Several web application vulnerabilities, such as … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 14] Web Applications I’m dreaming of secure web apps

Elf McSkidy was sipping her coffee when she saw on her calendar that it was time to review the web application’s security. An internal web application is being developed to be used internally and manage the cyber security team. She calls Elf Exploit McRed and asks him to check the in-development web application for common … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 13] Packet Analysis Simply having a wonderful pcap time

 After receiving the phishing email on Day 6 and investigating malware on Day 12, it seemed everything was ready to go back to normal. However, monitoring systems started to show suspicious traffic patterns just before closing the case. Now Santa’s SOC team needs help in analysing these suspicious network patterns. Learning Objectives Learn what … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 12] Malware Analysis Forensic McBlue to the REVscue!

  The malicious document attached to the phishing email was confirmed to have been executed. Aside from the fact that rogue connections were observed, we know little about what it does. Our in-house expert Forensic McBlue confirmed that the malicious document spawned another suspicious binary. Pivoting from that, he dumped it from memory for this task … Read more

[Video] TryHackMe Advent of Cyber 2022 – [Day 11] Memory Forensics Not all gifts are nice

The elves in Santa’s Security Operations Centre (SSOC) are hard at work checking their monitoring dashboards when Elf McDave, one of the workshop employees, knocks on the door. The elf says, “I’ve just clicked on something and now my workstation is behaving in all kinds of weird ways. Can you take a look?”. Elf McSkidy tasks you, … Read more