Situational Alert on recent Cyber Threats [cirt.gov.bd]
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team

Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
Source: Read More News, Security Advisories & Alerts BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team
সাম্প্রতিক সময়ে বাংলাদেশে সংঘটিত একাধিক সাইবার আক্রমনে র্যানসমওয়্যার, ওয়েব ডিফেসমেন্ট, তথ্য ফাঁস এবং ব্যক্তিগত সনাক্তকরণযোগ্য তথ্য (PII) চুরি, এসবের প্রবণতা বৃদ্ধি পেয়েছে। এমতাবস্থায় সরকারের সকল গুরুত্বপূর্ণ তথ্য পরিকাঠামো (CII), ব্যাংক, আর্থিক প্রতিষ্ঠান, স্বাস্থ্যসেবা প্রতিষ্ঠান এবং সরকারি ও বেসরকারি সংস্থাগুলোর সাইবার নিরাপত্তা নিশ্চিত করা আবশ্যক। এলক্ষ্যে BGD e-GOV CIRT বর্ণিত সকল সংস্থাকে সাইবার নিরাপত্তা ব্যবস্থাপনা জোরদার … Read more
সাম্প্রতিক সময়ে বাংলাদেশে সংঘটিত একাধিক সাইবার আক্রমনে র্যানসমওয়্যার, ওয়েব ডিফেসমেন্ট, তথ্য ফাঁস এবং ব্যক্তিগত সনাক্তকরণযোগ্য তথ্য (PII) চুরি, এসবের প্রবণতা বৃদ্ধি পেয়েছে। এমতাবস্থায় সরকারের সকল গুরুত্বপূর্ণ তথ্য পরিকাঠামো (CII), ব্যাংক, আর্থিক প্রতিষ্ঠান, স্বাস্থ্যসেবা প্রতিষ্ঠান এবং সরকারি ও বেসরকারি সংস্থাগুলোর সাইবার নিরাপত্তা নিশ্চিত করা আবশ্যক। এলক্ষ্যে BGD e-GOV CIRT বর্ণিত সকল সংস্থাকে সাইবার নিরাপত্তা ব্যবস্থাপনা জোরদার … Read more
Web defacement attacks and the exploitation of web application vulnerabilities are growing concerns in Bangladesh. These attacks, similar to virtual vandalism, involve hackers altering website appearances or content, often to embarrass site owners or promote personal agendas. Hackers also inject harmful code into websites, risking the security of visitor data. The exploitation of these vulnerabilities … Read more
Web defacement attacks and the exploitation of web application vulnerabilities are growing concerns in Bangladesh. These attacks, similar to virtual vandalism, involve hackers altering website appearances or content, often to embarrass site owners or promote personal agendas. Hackers also inject harmful code into websites, risking the security of visitor data. The exploitation of these vulnerabilities … Read more
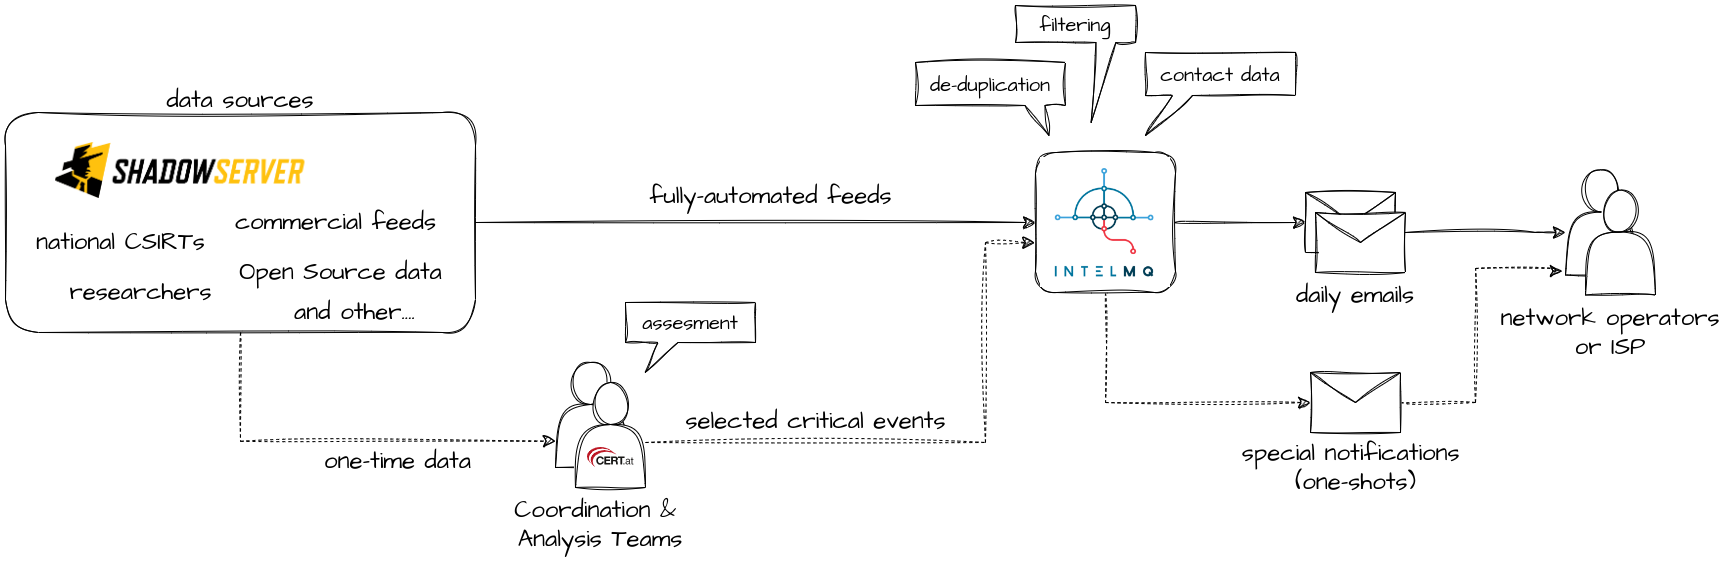
As a national CERT, one of our extremely important tasks is to proactively inform network operators about potential or confirmed security issues that could affect Austrian companies. Initially, I intended to discuss the technical changes in our systems, but I believe it’s better to start by explaining what we actually do and how we help … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more
An OS command injection vulnerability has been identified in the “less” utility, stemming from mishandling of quoting in `filename.c`. “less” is a text file viewer similar to “more” but allows users to move both backward and forward through files. It also starts faster than traditional text editors because it does not load the entire input … Read more