
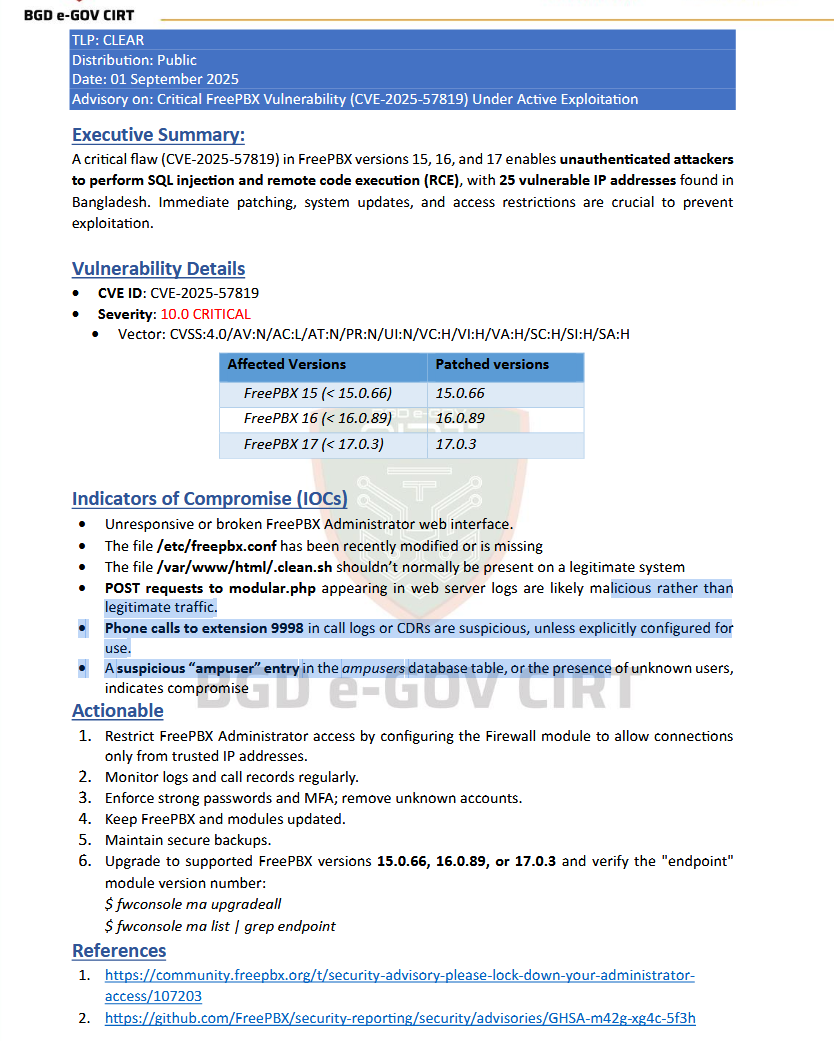
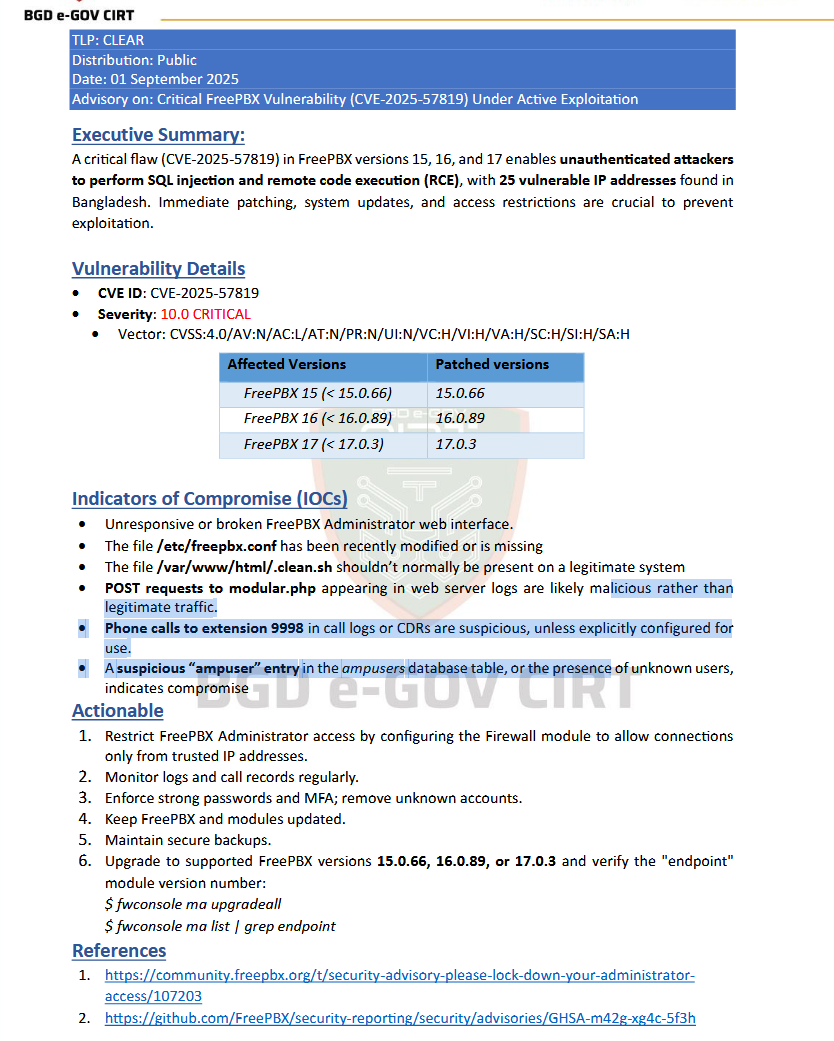
A critical flaw (CVE-2025-57819) in FreePBX versions 15, 16, and 17 enables unauthenticated attackers to perform SQL injection and remote code execution (RCE), with 25 vulnerable IP addresses found in Bangladesh. Immediate patching, system updates, and access restrictions are crucial to prevent exploitation.
Download the full PDF Document
Source: Read More
Security Advisories & Alerts
BGD e-GOV CIRT | Bangladesh e-Government Computer Incident Response Team